%59%6f%6e%67%64%61%65%20%4b%69%6d
-
 Devilray Exposes Blind Spots in FBS Detection
DAEJEON, South Korea — Governments use them to track phones. Criminals drive them through city streets and send texts that look like they came from your bank. For 20 years, researchers have been building tools to catch these fake cell towers. They have tested those tools mostly against fake towers they built themselves.
That loop has left gaps. Researchers at KAIST built a platform called Devilray that reproduces 2,592 distinct fake-base-station behaviors. They ran it against seven existing detection systems, and every one of them missed at least 192. The finding points to a larger problem with how the field tests itself: detectors have been evaluated against the wrong adversary.
An echo chamber
Fake base stations go by several names: IMSI catchers, cell-site simulators, StingRays. They pose as legitimate cell towers and get nearby phones to connect. Once a phone is connected, the fake tower can make it give up the identifier that ties it to its owner or reveal where it is. It can also cut the phone off, push it down to an older and weaker network, or send it messages that never passed through a carrier. Police and intelligence agencies have used these devices for surveillance for years. Criminals now use them for illegal surveillance and for SMS-blaster scams, in which a device carried in a car sends phishing texts to every phone nearby.
The commercial machines are expensive, and their sale and operation are tightly restricted. Universities generally cannot buy one. Carriers and investigative agencies are the ones responsible for finding fake towers in the field, but even they cannot get every model, let alone every new variant.
So researchers do the reasonable thing. They build a fake base station, study the traces it leaves, design a detector that recognizes those traces and report that it works. The next paper improves on the last one, and detection rates climb.
But the attacker in those experiments is one the defender already knows. The attack used to design a detector and the attack used to test it rest on the same assumptions. A detector that scores well may simply be recognizing its own reflection. What the field has lacked, the researchers argue, is adversarial thinking. The question should not be whether a detector catches a known attack. It should be what an attacker would do instead.
"Detection has been built around the attacks we already know," said Yongdae Kim, the KAIST professor of electrical engineering who led the work. "Real attackers don't stay there. Until now, the playing field has tilted toward them."
A standard full of open doors
Attackers have that much room because of how LTE works. When an LTE phone first connects, it does not check whether the base station is genuine. It acts on some messages before any authentication takes place, and it can be pushed down to older generations of network. These are not implementation bugs that a patch can fix. They are written into the standard, so an attacker can choose from many messages and stay fully standard-compliant.
Take the phone's permanent identifier, the main prize for a surveillance device. A fake tower can simply ask for it. That request is the move that Rayhunter, the Electronic Frontier Foundation's open-source detector, watches for. The tower can also send a rejection message that makes the phone reconnect and hand over the identifier without being asked. The standard allows both. A detector watching one door does not see the other.
"LTE is fundamentally broken," Professor Kim said. "It is full of standard-compliant messages that can be used for bad purposes."
Nobody is going to fix that. LTE's security design was settled long ago, and the standards community has moved on to 5G. Yet LTE remains the backbone of mobile service in most of the world. Many 5G networks still lean on it, and 5G phones drop back to LTE whenever 5G is unavailable, or whenever an attacker forces them to. These weaknesses will stay in the field as long as LTE does. As a result, defending against fake base stations looks less like fixing a software bug and more like an ongoing contest: a new attack appears, a detector learns to catch it, the attacker changes. That contest only works if defenders can see the moves attackers are able to make.
Thinking like the attacker
Devilray reverses the usual order. It maps the attacker first and looks at the detectors only afterward.
The team began with a commercial fake base station, a unit sold to law enforcement and intelligence agencies. It is the first such device to be analyzed in an academic study. The device could do several things that academic prototypes rarely model:
• copy the identity of a legitimate tower,
• hop between frequencies,
• run two networks at once,
• dial its power down to cover only a few meters.
The researchers then looked past that single device. They went through prior research and the 3GPP standards that govern cellular networks for other routes to the same ends. They broke a fake-base-station operation into four stages: surveying the local network, launching a fake cell, luring phones to connect, and carrying out the attack. Across those stages they identified seven dimensions an attacker can vary. Twenty-one dependency rules remove combinations that could not occur together in a real exchange. What remained were 2,592 configurations.
Every configuration was then run against real smartphones to confirm that the full procedure completed. That check matters in both directions. An attack space derived only from the specifications could include thousands of combinations no phone would actually accept. A baseline copied from a single commercial device would inherit that device's limits. Devilray is anchored in the real device and extends outward into behaviors the standard permits.
The researchers stress that 2,592 is not a count of attacks seen in the wild, and not a list of 2,592 ways to beat every detector. It is something the field has not had before: a realistic adversary, grounded in a real device and the standard itself, against which detectors can finally be tested.
Seven detectors, seven sets of blind spots
The seven detectors the team tested are publicly available and work on different principles: signaling messages, base station information, radio signals, statistical patterns and machine learning. Every one had blind spots, and most traced back to an assumption built into its design.
Some detectors key on one telltale message, so they missed attacks that reached the same goal by another route. Others flag the unusually strong signal of a cheap fake tower; a fake tower that turns its power down, as the commercial unit can, stays under their thresholds. One statistical detector watches how often phones in an area are asked to reveal their identifiers. A fake tower that collects identifiers patiently, from a fraction of the phones nearby instead of all of them, produced a pattern that looked like an ordinary bus terminal.
The harder question
The deepest blind spot is the one where the attack starts to look like a normal network. The researchers tested this directly. They retrained a machine-learning detector on the Devilray attacks it had missed. On the radio link layer (RRC) model, its detection rate rose from 51 percent to 96 percent, while its false-alarm rate on ordinary carrier traffic nearly quadrupled, from 1.4 percent to 5.3 percent. On the core network layer (NAS) model, the detection rate rose from 27 percent to 63 percent, and its false-alarm rate increased from 4.7 percent to 8.8 percent. When trained on the hardest case, that false-alarm rate reached 15 percent, particularly for the NAS layer model.
A detector that catches everything but constantly flags ordinary networks is of little use, and neither is a quiet one that misses carefully chosen attacks. The problem is not simply to maximize detection. It is to find the boundary between malicious and legitimate behavior when the standard lets an attacker move right up against it.
"The real question is whether we can reduce misses without raising false alarms," Professor Kim said.
The researchers argue that future detectors should report both numbers together. Claiming better coverage without testing against ordinary traffic gives an incomplete picture of whether a detector can actually be deployed.
An attacker for defenders
A platform that can imitate thousands of attack behaviors could also be misused, and the researchers acknowledge the risk. They share Devilray only with vetted researchers and organizations, under controlled access. What defenders have lacked is the same range of behavior to test against. With Devilray, carriers, investigators and detector developers can do that without having to buy every device on the market.
The name is a jab at the StingRay, the commercial device whose name became shorthand for the whole category. A devil ray is a much bigger relative.
The work is already reaching defenders. The team gave EFF the attack cases Rayhunter misses, and the foundation is now working on ways to detect them. The GSMA, the global association of mobile operators, invited the researchers to present Devilray to its Fraud and Security Group. There, standards and industry representatives discussed where fake-base-station detection should go next.
The study was led by KAIST in collaboration with South Korea's National Security Research Institute, Kyung Hee University, the University of Florida and Cape, a U.S. mobile network company. It will be presented in December at ACSAC 2026 in Los Angeles.
Professor Kim's group is now building a detection system of its own. No single vantage point may see enough, so it combines what phones observe, what carriers can see inside their networks and what independent radio sniffers capture. The aim is to detect fake base stations and also to locate them.
"Devilray is not meant to defeat existing detectors," Professor Kim said. "It gives defenders the same choices attackers already have, so that attack and defense can finally advance together."
Paper: "Devilray: A Reconfigurable Adversarial Baseline for Revealing Blind Spots in Fake Base Station Detection," IEEE ACSAC 2026, Los Angeles, Dec. 7–11, 2026. arXiv: https://arxiv.org/abs/2605.19232 · Project page and demo videos: https://sites.google.com/view/devilray
Access: Devilray is available to vetted researchers and organizations under controlled access. Requests: https://sites.google.com/view/devilray
Authors: Led by KAIST — Taekkyung Oh and Duckwoo Kim (co-first authors), Beomseok Oh and Yongdae Kim (KAIST); Hansung Bae and Byeongdo Hong (National Security Research Institute); CheolJun Park (Kyung Hee University); Tyler Tucker, Nathaniel Bennett and Patrick Traynor (University of Florida); Sangwook Bae (Cape).
Funding: Institute of Information & communications Technology Planning & Evaluation (IITP) grant funded by the Korea government(MSIT) (No. RS-2024-00441762, Global Advanced Cybersecurity Human Resources Development).
Contact: Professor Yongdae Kim, School of Electrical Engineering, KAIST · yongdaek@kaist.ac.kr
2026.11.04 View 1231
-
 KAIST Researchers Uncover Critical Security Flaws in Global Mobile Networks
Breakthrough Discovery Reveals How Attackers Can Remotely Manipulate User Data Without Physical Proximity
DAEJEON, South Korea — In an era when recent cyberattacks on major telecommunications providers have highlighted the fragility of mobile security, researchers at the Korea Advanced Institute of Science and Technology have identified a class of previously unknown vulnerabilities that could allow remote attackers to compromise cellular networks serving billions of users worldwide.
The research team, led by Professor Yongdae Kim of KAIST's School of Electrical Engineering, discovered that unauthorized attackers could remotely manipulate internal user information in LTE core networks — the central infrastructure that manages authentication, internet connectivity, and data transmission for mobile devices and IoT equipment.
The findings, presented at the 32nd ACM Conference on Computer and Communications Security in Taipei, Taiwan, earned the team a Distinguished Paper Award, one of only 30 such honors selected from approximately 2,400 submissions to one of the field's most prestigious venues.
A New Class of Vulnerability
The vulnerability class, which the researchers termed "Context Integrity Violation" (CIV), represents a fundamental breach of a basic security principle: unauthenticated messages should not alter internal system states. While previous security research has primarily focused on "downlink" attacks — where networks compromise devices — this study examined the less-scrutinized "uplink" security, where devices can attack core networks.
"The problem stems from gaps in the 3GPP standards," Professor Kim explained, referring to the international body that establishes operational rules for mobile networks. "While the standards prohibit processing messages that fail authentication, they lack clear guidance on handling messages that bypass authentication procedures entirely."
The team developed CITesting, the world's first systematic tool for detecting these vulnerabilities, capable of examining between 2,802 and 4,626 test cases — a vast expansion from the 31 cases covered by the only previous comparable research tool, LTEFuzz.
Widespread Impact Confirmed
Testing four major LTE core network implementations — both open-source and commercial systems — revealed that all contained CIV vulnerabilities. The results showed:
Open5GS: 2,354 detections, 29 unique vulnerabilities
srsRAN: 2,604 detections, 22 unique vulnerabilities
Amarisoft: 672 detections, 16 unique vulnerabilities
Nokia: 2,523 detections, 59 unique vulnerabilities
The research team demonstrated three critical attack scenarios: denial of service by corrupting network information to block reconnection; IMSI exposure by forcing devices to retransmit user identification numbers in plaintext; and location tracking by capturing signals during reconnection attempts.
Unlike traditional attacks requiring fake base stations or signal interference near victims, these attacks work remotely through legitimate base stations, affecting anyone within the same MME (Mobility Management Entity) coverage area as the attacker — potentially spanning entire metropolitan regions.
Industry Response and Future Implications
Following responsible disclosure protocols, the research team notified affected vendors. Amarisoft deployed patches, and Open5GS integrated the team's fixes into its official repository. Nokia, however, stated it would not issue patches, asserting compliance with 3GPP standards and declining to comment on whether telecommunications companies currently use the affected equipment.
"Uplink security has been relatively neglected due to testing difficulties, implementation diversity, and regulatory constraints," Professor Kim noted. "Context integrity violations can pose serious security risks."
The research team, which included KAIST doctoral students Mincheol Son and Kwangmin Kim as co-first authors, along with Beomseok Oh and Professor CheolJun Park of Kyung Hee University, plans to extend their validation to 5G and private 5G environments. The tools could prove particularly critical for industrial and infrastructure networks, where breaches could have consequences ranging from communication disruption to exposure of sensitive military or corporate data.
The research was supported by the Ministry of Science and ICT through the Institute for Information & Communications Technology Planning & Evaluation, as part of a project developing security technologies for 5G private networks.
With mobile networks forming the backbone of modern digital infrastructure, the discovery underscores the ongoing challenge of securing systems designed in an era when such sophisticated attacks were barely conceivable — and the urgent need for updated standards to address them.
2025.11.03 View 7894
-
 Vulnerability Found: One Packet Can Paralyze Smartphones
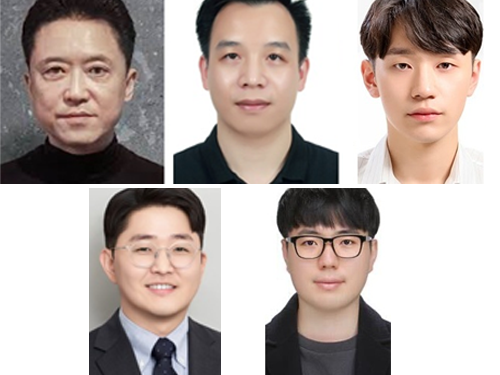
<(From left) Professor Yongdae Kim, PhD candidate Tuan Dinh Hoang, PhD candidate Taekkyung Oh from KAIST, Professor CheolJun Park from Kyung Hee University; and Professor Insu Yun from KAIST>
Smartphones must stay connected to mobile networks at all times to function properly. The core component that enables this constant connectivity is the communication modem (Baseband) inside the device. KAIST researchers, using their self-developed testing framework called 'LLFuzz (Lower Layer Fuzz),' have discovered security vulnerabilities in the lower layers of smartphone communication modems and demonstrated the necessity of standardizing 'mobile communication modem security testing.'
*Standardization: In mobile communication, conformance testing, which verifies normal operation in normal situations, has been standardized. However, standards for handling abnormal packets have not yet been established, hence the need for standardized security testing.
Professor Yongdae Kim's team from the School of Electrical Engineering at KAIST, in a joint research effort with Professor CheolJun Park's team from Kyung Hee University, announced on the 25th of July that they have discovered critical security vulnerabilities in the lower layers of smartphone communication modems. These vulnerabilities can incapacitate smartphone communication with just a single manipulated wireless packet (a data transmission unit in a network). In particular, these vulnerabilities are extremely severe as they can potentially lead to remote code execution (RCE)
The research team utilized their self-developed 'LLFuzz' analysis framework to analyze the lower layer state transitions and error handling logic of the modem to detect security vulnerabilities. LLFuzz was able to precisely extract vulnerabilities caused by implementation errors by comparing and analyzing 3GPP* standard-based state machines with actual device responses.
*3GPP: An international collaborative organization that creates global mobile communication standards.
The research team conducted experiments on 15 commercial smartphones from global manufacturers, including Apple, Samsung Electronics, Google, and Xiaomi, and discovered a total of 11 vulnerabilities. Among these, seven were assigned official CVE (Common Vulnerabilities and Exposures) numbers, and manufacturers applied security patches for these vulnerabilities. However, the remaining four have not yet been publicly disclosed.
While previous security research primarily focused on higher layers of mobile communication, such as NAS (Network Access Stratum) and RRC (Radio Resource Control), the research team concentrated on analyzing the error handling logic of mobile communication's lower layers, which manufacturers have often neglected.
These vulnerabilities occurred in the lower layers of the communication modem (RLC, MAC, PDCP, PHY*), and due to their structural characteristics where encryption or authentication is not applied, operational errors could be induced simply by injecting external signals.
*RLC, MAC, PDCP, PHY: Lower layers of LTE/5G communication, responsible for wireless resource allocation, error control, encryption, and physical layer transmission.
The research team released a demo video showing that when they injected a manipulated wireless packet (malformed MAC packet) into commercial smartphones via a Software-Defined Radio (SDR) device using packets generated on an experimental laptop, the smartphone's communication modem (Baseband) immediately crashed
※ Experiment video: https://drive.google.com/file/d/1NOwZdu_Hf4ScG7LkwgEkHLa_nSV4FPb_/view?usp=drive_link
The video shows data being normally transmitted at 23MB per second on the fast.com page, but immediately after the manipulated packet is injected, the transmission stops and the mobile communication signal disappears. This intuitively demonstrates that a single wireless packet can cripple a commercial device's communication modem.
The vulnerabilities were found in the 'modem chip,' a core component of smartphones responsible for calls, texts, and data communication, making it a very important component.
Qualcomm: Affects over 90 chipsets, including CVE-2025-21477, CVE-2024-23385.
MediaTek: Affects over 80 chipsets, including CVE-2024-20076, CVE-2024-20077, CVE-2025-20659.
Samsung: CVE-2025-26780 (targets the latest chipsets like Exynos 2400, 5400).
Apple: CVE-2024-27870 (shares the same vulnerability as Qualcomm CVE).
The problematic modem chips (communication components) are not only in premium smartphones but also in low-end smartphones, tablets, smartwatches, and IoT devices, leading to the widespread potential for user harm due to their broad diffusion.
Furthermore, the research team experimentally tested 5G vulnerabilities in the lower layers and found two vulnerabilities in just two weeks. Considering that 5G vulnerability checks have not been generally conducted, it is possible that many more vulnerabilities exist in the mobile communication lower layers of baseband chips.
Professor Yongdae Kim explained, "The lower layers of smartphone communication modems are not subject to encryption or authentication, creating a structural risk where devices can accept arbitrary signals from external sources." He added, "This research demonstrates the necessity of standardizing mobile communication modem security testing for smartphones and other IoT devices."
The research team is continuing additional analysis of the 5G lower layers using LLFuzz and is also developing tools for testing LTE and 5G upper layers. They are also pursuing collaborations for future tool disclosure. The team's stance is that "as technological complexity increases, systemic security inspection systems must evolve in parallel."
First author Tuan Dinh Hoang, a Ph.D. student in the School of Electrical Engineering, will present the research results in August at USENIX Security 2025, one of the world's most prestigious conferences in cybersecurity.
※ Paper Title: LLFuzz: An Over-the-Air Dynamic Testing Framework for Cellular Baseband Lower Layers (Tuan Dinh Hoang and Taekkyung Oh, KAIST; CheolJun Park, Kyung Hee Univ.; Insu Yun and Yongdae Kim, KAIST)
※ Usenix paper site: https://www.usenix.org/conference/usenixsecurity25/presentation/hoang (Not yet public), Lab homepage paper: https://syssec.kaist.ac.kr/pub/2025/LLFuzz_Tuan.pdf
※ Open-source repository: https://github.com/SysSec-KAIST/LLFuzz (To be released)
This research was conducted with support from the Institute of Information & Communications Technology Planning & Evaluation (IITP) funded by the Ministry of Science and ICT.
2025.07.25 View 8682
-
 3rd KAIST Junghoon Cho Academic Award Ceremony
3rd KAIST Junghoon Cho Academic Award CeremonyAcademic award to Sehoon Kim, scholarship to Yougdae Kim, Daehyun Kim, Sunchul Park
KAIST (President Nam Pyo Suh) had the 3rd KAIST Junghoon Cho Academic Award ceremony at the conference room in the main administration building, Friday, May 11, at 2 pm with President Suh and the bereaved family attended.
Sehoon Kim, a doctoral researcher at the Agency for Defense Development (ADD) and KAIST graduate, was named as the 3rd recipient of the Junghoon Cho Academic Award in recognition of his achievement that establishes the design method of supersonic vacuum device. The scholarship was granted to Yongdae Kim (doctoral student of Aerospace Engineering, KAIST), Daehyun Kim (master student of Mechanical Engineering, Korea University), and Suncheol Park (senior of the Attached High School to the College of Education at kongju National University). The prize money is 20 million won, and the scholarship amounts to 3 million and 2 million won for university and high school students, respectively.
“Junghoon Cho Academic Award” is a meaningful award established by the donation of compensation money and personal properties, amounting to about 470 billion won, by Donggil Cho, father of the late Ph.D. Junghoon Cho who died at the explosion accident at the Wind Tunnel Laboratory in 2002, ▲ Ph.D. Sehonn Kim
2007.05.14 View 22336